Solution Architecture
The EXO Lab demonstrates how Microsoft 365 security technologies can be
integrated into an automated incident detection, response, reporting,
and analytics solution.
High-Level Data Flow
📧
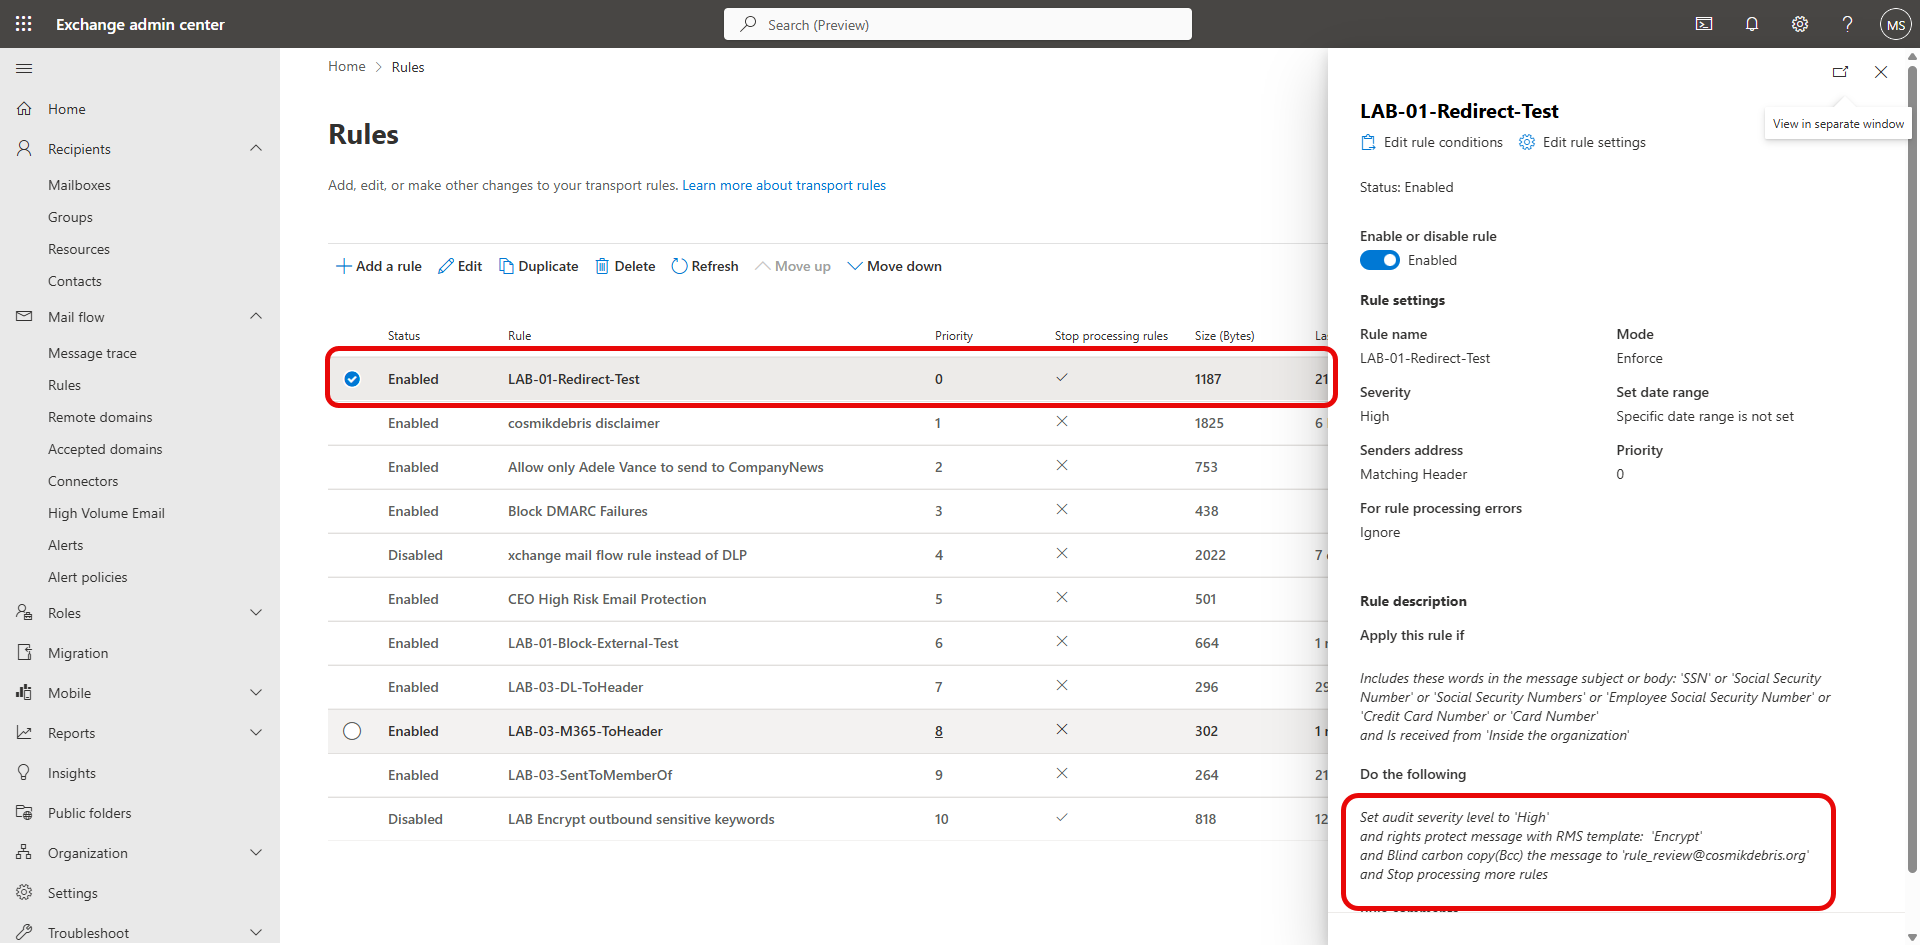
Exchange Online
Email Processing & Mail Flow
↓
🛡️
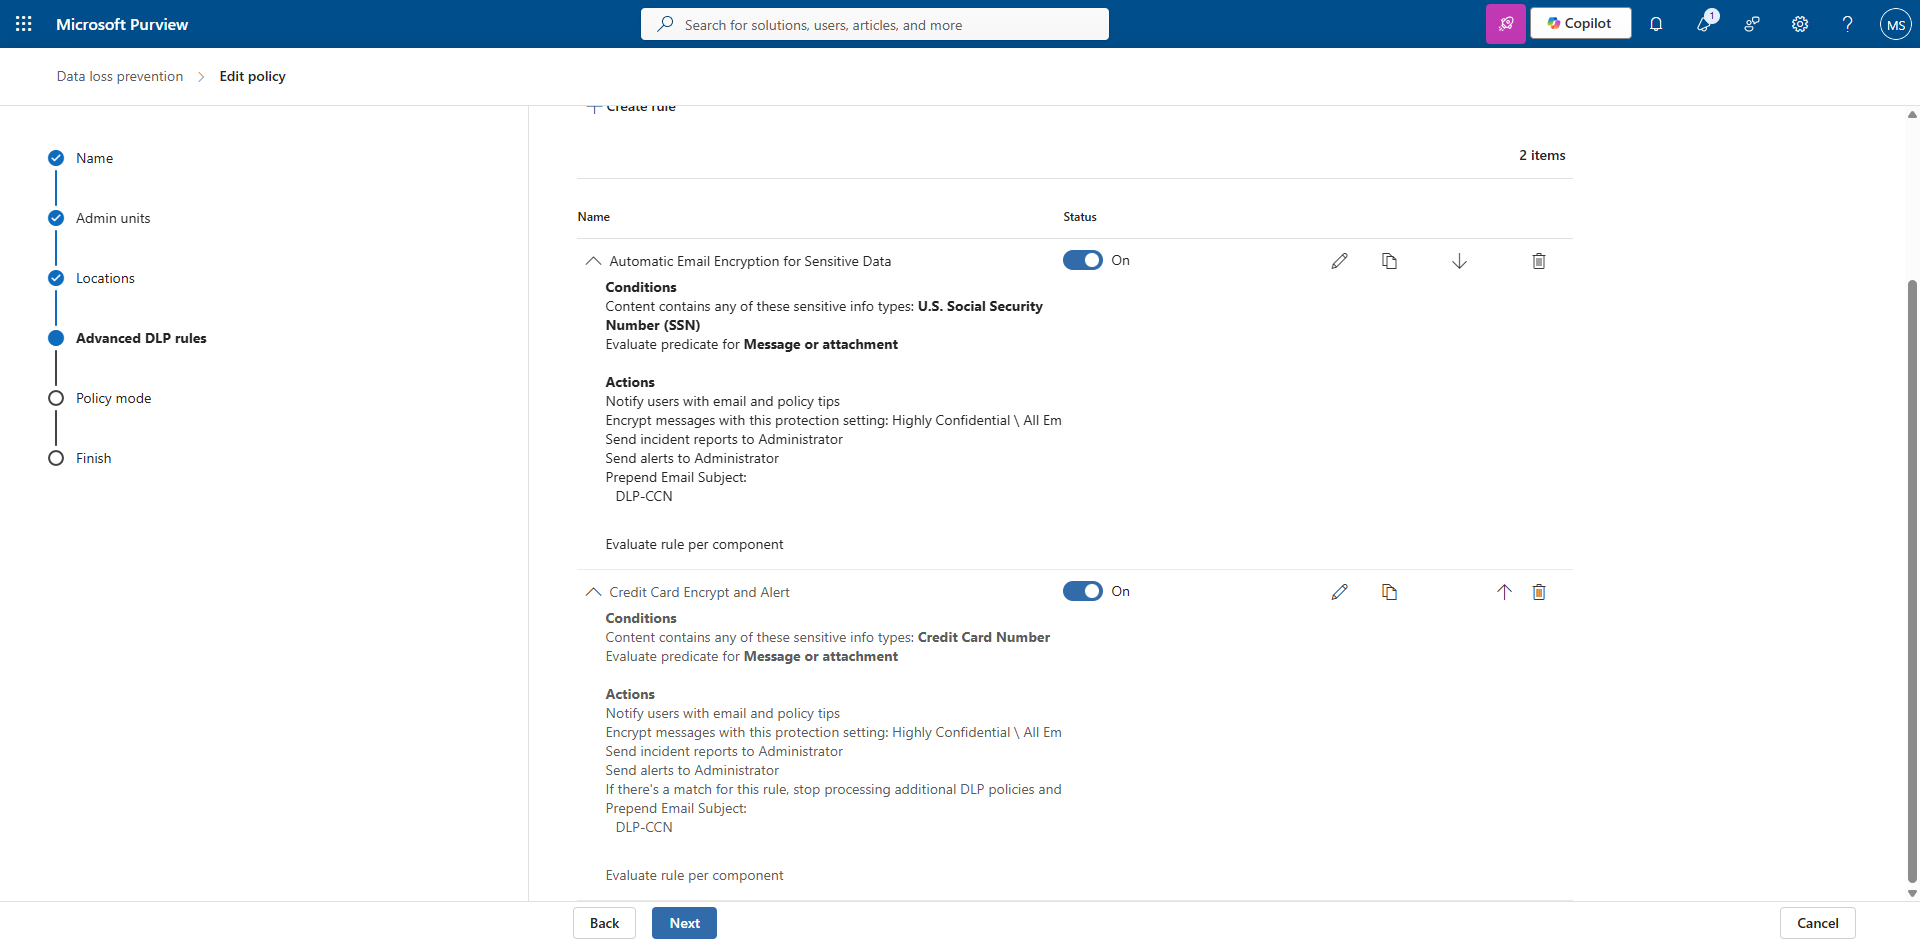
Microsoft Purview DLP
Policy Evaluation & Sensitive Data Detection
↓
⚡
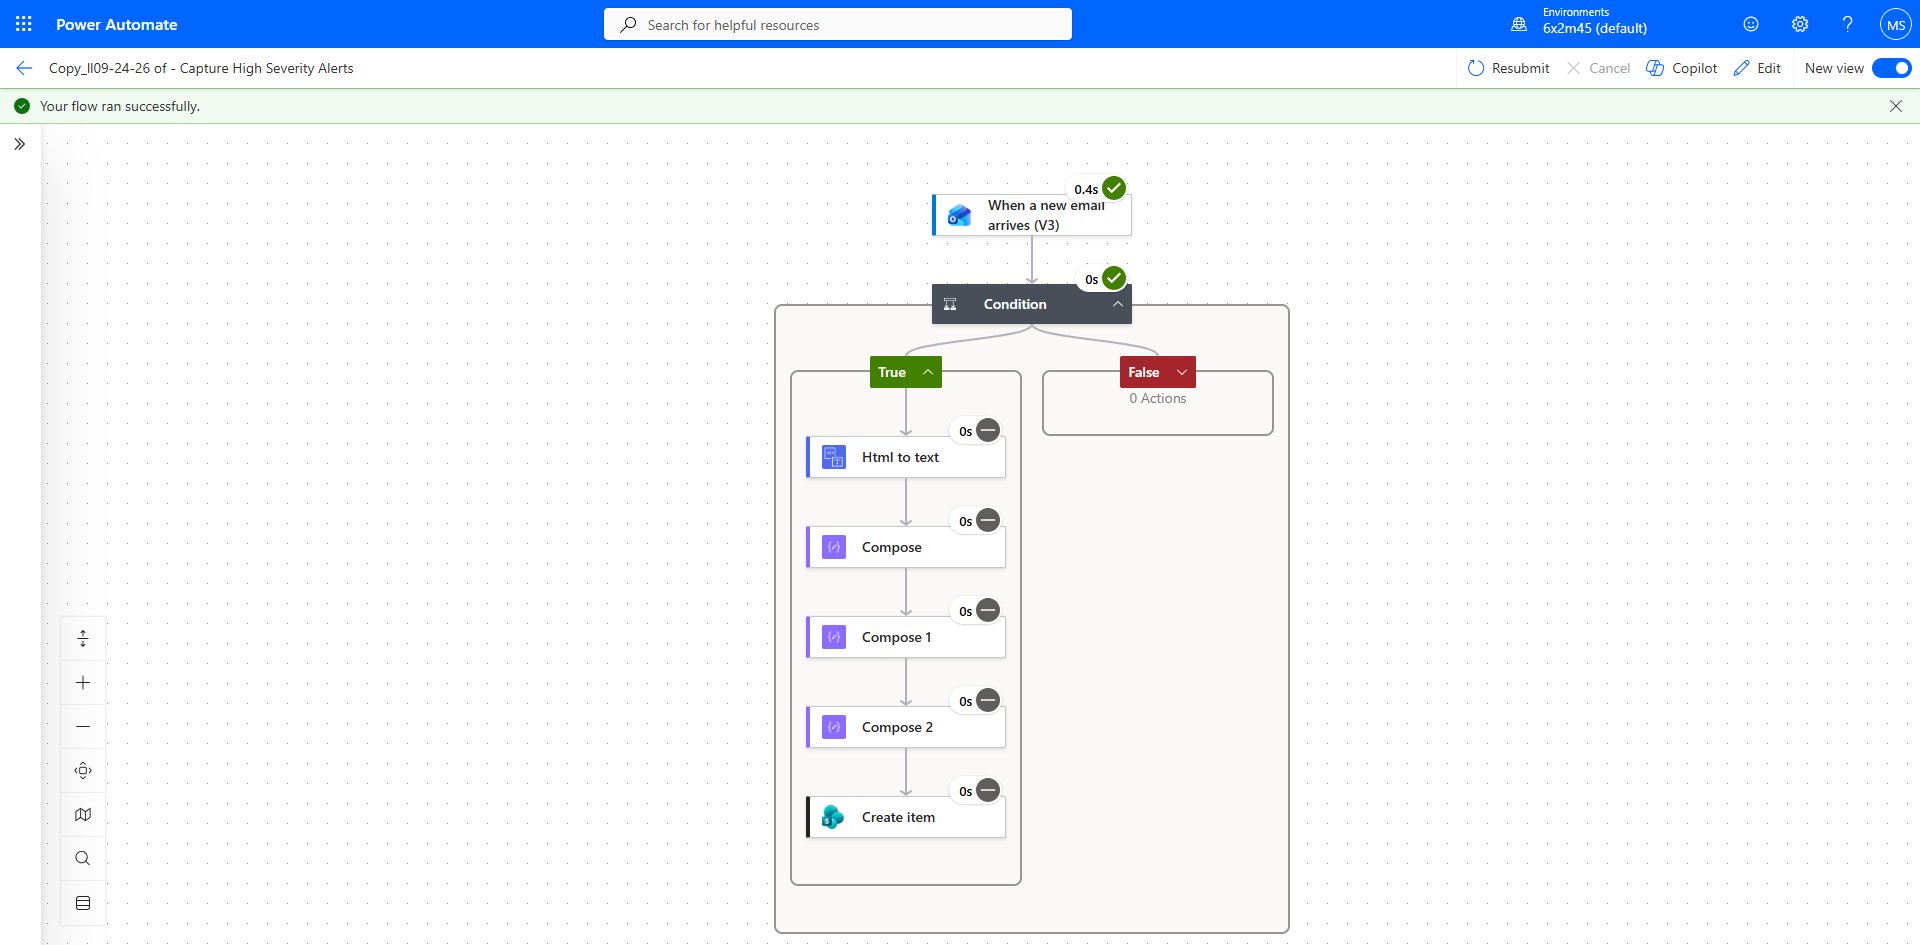
Power Automate
Workflow Automation & Alert Processing
↓
📂
SharePoint Online
Incident Repository
↓
📊
Power BI Dashboard
Executive Dashboard & Reporting
Incident Processing Workflow
-
An email is sent or received through Exchange Online.
-
Microsoft Purview Data Loss Prevention policies inspect message
content for sensitive information.
-
A policy match generates an alert event.
-
Power Automate processes the alert and extracts relevant metadata.
-
Event details are written to a SharePoint Online incident repository.
-
Power BI consumes the SharePoint dataset and provides
security analytics, trending, and reporting.
Core Components
Exchange Online
Provides enterprise email services and enforcement of transport and
encryption rules used to protect sensitive information.
Microsoft Purview DLP
Detects sensitive information such as PII, financial data,
and compliance-related content using configurable policies.
Power Automate
Automates alert processing and eliminates manual collection of
incident details.
SharePoint Online
Acts as a centralized repository for high-severity security events
and compliance alerts.
Power BI Dashboard
Visualizes incident trends, policy activity, severity distribution,
and operational metrics for management reporting.
Security Controls Demonstrated
- Exchange Online Mail Flow Rules
- Email Encryption Policies
- Microsoft Purview DLP Policies
- Automated Incident Processing
- SharePoint Incident Tracking
- Power BI Security Analytics
- Microsoft 365 Security Operations Concepts
Future Expansion
Phase III will extend the architecture through Microsoft Sentinel
integration, providing centralized SIEM monitoring, threat
correlation, advanced alerting, and enterprise security analytics.
Exchange Online
↓
Purview DLP
↓
Power Automate
↓
SharePoint Online
↓
Power BI
↓
Microsoft Sentinel